AI-Driven Security Operations
AI at the core of your SOC — and zero trust around the AI you run.
Our Advanced MDR tier puts machine-learning behaviour analytics, an AI / ML SIEM and automated response at the centre of detection. The same zero-trust controls then extend to the AI agents, models and data pipelines your business is deploying.
9
Domains: Identity to next-gen architecture
4
Clouds + on-prem: AWS, Azure, Google Cloud, Oracle Cloud
10+
Frameworks: Global and regional compliance supported
24×7
365 Days: Global SOC coverage, three managed tiers
Security Powered by AI
INCLUDED IN ADVANCED MDR · GSOC 24×7×365

Behaviour Analytics (UEBA)

AI/ML SIEM Correlation

Automated Response (SOAR)

Threat Intelligence and Research
Security for AI
PART OF THE ZERO-TRUST REFERENCE ARCHITECTURE

AI-Agent Identities

AI Workloads and APIs

Data for AI

AI Risk and Governance
- Humans stay in the loop. AI handles the volume — correlation, enrichment and routine containment. GSOC analysts approve high-impact actions, hunt what models cannot yet see, and feed every confirmed case back into detection.
Security Services Portfolio
A sequence you can enter at any stage: a fixed-fee assessment, a milestone-based build, or a subscription managed detection and response service with three SOC tiers.
1. Assess & Advise
One-time · Fixed fee
- Cyber Security Assessment
- Penetration Testing
- Application Security (DAST / SAST)
- Attack Surface Discovery
- Strategic Advisory & Proof of Concept
2. Build & Transform
Project · Milestone-based
- SOC build & build-operate-transfer
- On-premise to cloud migration
- Zero-trust architecture & SASE
- Identity & access (IDAM, PAM, UAM)
- Security tools & data centre consolidation
3. Run
Managed Detection & Response
Subscription · 24×7×365
- Managed SOC (Basic) – SIEM, log management and 24×7 monitoring, triage and alerting.
- Managed SOC (Standard) – Everything in Basic, plus threat hunting, vulnerability and firewall management, and automated response.
- Advanced MDR – Everything in Standard, plus AI / ML behaviour analytics, a threat intelligence platform and dedicated threat research.
4. Govern & Assure
Across Every Stage
Continuous · Retainer
- Audit & Reporting Support
- vCISO & Security Leadership
- Security Posture Management
- Risk & Compliance
One-time · Fixed fee
- Cyber Security Assessment
- Penetration Testing
- Application Security (DAST / SAST)
- Attack Surface Discovery
- Strategic Advisory & Proof of Concept
Project · Milestone-based
- SOC build & build-operate-transfer
- On-premise to cloud migration
- Zero-trust architecture & SASE
- Identity & access (IDAM, PAM, UAM)
- Security tools & data centre consolidation
Managed Detection & Response
Subscription · 24×7×365
- Managed SOC (Basic) – SIEM, log management and 24×7 monitoring, triage and alerting.
- Managed SOC (Standard) – Everything in Basic, plus threat hunting, vulnerability and firewall management, and automated response.
- Advanced MDR – Everything in Standard, plus AI / ML behaviour analytics, a threat intelligence platform and dedicated threat research.
Across Every Stage
Continuous · Retainer
- Audit & Reporting Support
- vCISO & Security Leadership
- Security Posture Management
- Risk & Compliance
Cyber Security Domains

Identity Security
User lifecycle (JML) · SSO & federation · CIAM · MFA · PIM / PAM

Endpoint Security
Malware protection · Host IDS / IPS · Endpoint DLP · Disk encryption & FIM

Application Security
SAST · DAST · SCA · IAST · DevSecOps CI / CD · Pen testing · Virtual patching

Network Security
NG firewall & DDoS · WAF · IDS / IPS & NDR · Email security · Bot protection
Data Security
Masking & obfuscation · DAM · KMS / HSM · Classification & DLP · DRM · PKI / CLM

Threat Management
AI / ML SIEM · SOAR & UEBA · Threat intel & hunting · EDR / XDR / MDR

Cloud Security
Native & third-party controls · Landing zone security · Posture management · Azure, AWS, GCP, OCI
Governance, Risk & Compliance
ISO 27k · GDPR · NIS2 · PCI DSS · NIST · CCPA · Enterprise & third-party risk
Next-Gen & Advisory
Zero trust · SASE / SSE · Container & IoT / OT security · CISO-as-a-service · SOC design & build
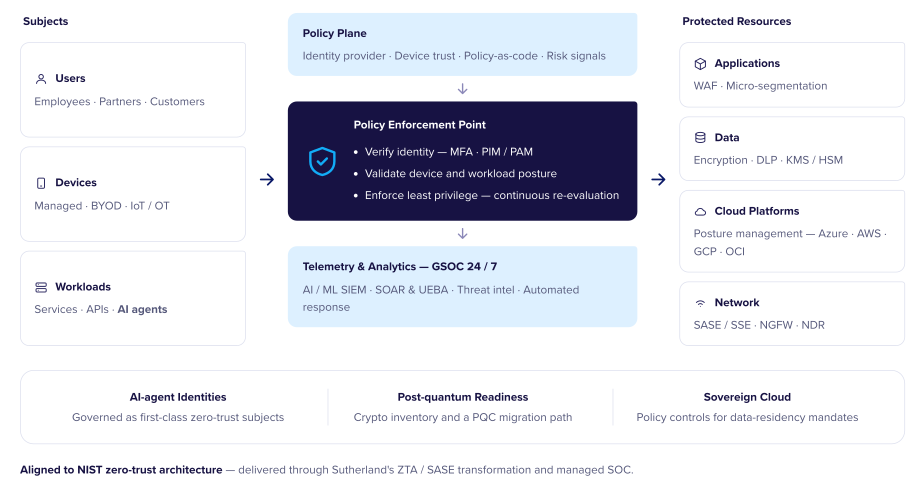
Zero-trust Reference Architecture – Never Trust, Always Verify.
Every request — from a person, a device or an AI agent — is evaluated against policy before it reaches a resource, and re-evaluated continuously while it holds access.
Coverage & Compliance
AWS | Microsoft | Azure | Google Cloud | Oracle Cloud | On-premise
Native and third-party controls with unified posture management across all four clouds and your data centres.
Fully managed | Co-managed | Build-operate-transfer | Advisory retainer
Run it for you, run it with you, or build it and hand it over — the model can change as your team matures.
ISO 27001 | NIST | PCI DSS | GDPR | HIPAA | NIS2 | CCPA | FedRAMP | CSA STAR | GxP | MAS | RBI | OJK | IRAP
Global and regional mandates covered by the Govern & assure retainer, with audit and reporting support included.
Why Sutherland
AI-Driven Global SOC
24×7×365 SOC with AI/ML SIEM, UEBA, SOAR, threat intelligence and human oversight.
Full Security-Estate Coverage
Assessment, architecture and operations across nine cyber security domains.
Zero-Trust by Design
Continuous verification and least privilege across users, devices, workloads and AI agents.
Hybrid & Multi-Cloud Security
Unified security across AWS, Azure, Google Cloud, Oracle Cloud and on-premise estates.
Flexible Delivery Models
Fully managed, co-managed, build-operate-transfer and advisory retainer models.
Continuous Governance
Security posture, risk, compliance, audit and reporting support across 10+ frameworks.